Agentic AI IT asset management connects ITAM, CMDB, endpoint, identity, logistics and policy data so AI agents can investigate unaccounted assets, reconcile conflicting records and take governed, verified action. This post explains the workflow, architecture, controls and outcomes of that operating model.
Executive Introduction
A missing laptop is rarely caused by one failed process. It appears when several systems hold fragments of the truth. The service desk shows an employee's assignment, endpoint management has no recent check-in, human resources shows that the employee has left, and a courier record says the package reached a regional office. Each record may be correct within its workflow, yet the enterprise still cannot answer who has the asset now.
This is the practical case for Agentic AI IT asset management. The goal is not to add another dashboard; it is to create asset intelligence that connects custody, location, identity, technical telemetry, procurement, service history, and policy into a decision-ready record. AI agents for IT asset management can then investigate exceptions, perform IT asset reconciliation, and take controlled action. For enterprises with many locations, mobile workforces, repair vendors, and intermittent connectivity, that operating model can reduce the time assets remain unaccounted for and improve confidence in the inventory used for security, finance, and compliance decisions.
Agentic AssetOps applies Agentic AI to this Agentic AI asset management problem. ElixirData provides trusted context, ElixirHub governs reusable operational skills, and ElixirClaw coordinates decisions and actions. The aim is autonomous asset operations with bounded authority: an agent should never infer that an asset is lost from one stale field. It must evaluate evidence, respect authority boundaries, record its decision, and verify the result.
See how Context OS governs AI agent decisions
Context OS gives asset agents trusted context, policy boundaries and decision traces before they change any record.
What Is the Real World Operational Challenge?
Consider a manufacturer with corporate offices, plants, distribution centers, field service teams, and third-party repair depots. A field engineer leaves the company and returns a laptop, mobile device, and diagnostic scanner to a branch office. The branch records the package, but the central asset register remains unchanged. The laptop later appears on the network under a staging account, the mobile device stops checking in, and the scanner is transferred to another engineer without a formal custody event.
The asset team now has three exceptions that look similar but require different decisions. The laptop is not lost; it is awaiting reissue. The mobile device may need a security response because its last known user is inactive, and its location is unknown. The scanner is operational, but the enterprise cannot prove its current custodian. A bulk status update would hide those distinctions. A manual investigation may find them, but it depends on people searching several systems, contacting local teams, interpreting timestamps, and deciding which record to trust.
The impact extends beyond replacement cost. Uncertain custody can delay onboarding, create duplicate purchases, leave licenses attached to inactive users, weaken audit evidence, and expose data on devices that should have been recovered or disabled. Finance may depreciate assets that no longer exist, while security cannot tell whether an offline endpoint is stored, stolen, decommissioned, or disconnected.
Why Does Traditional IT Asset Management Fall Short Across Distributed Locations?
Traditional IT asset management systems are valuable systems of record, but they depend on timely updates and process adherence. In distributed enterprises, the ITAM record may describe a state without explaining how it was reached or whether newer endpoint, identity, logistics, or site evidence contradicts it. Multiple CMDB instances, regional tools, local spreadsheets, and endpoint platforms may also identify the same device differently, making IT asset reconciliation and enterprise asset visibility difficult.
-
Data fragmentation prevents teams from seeing procurement, assignment, network, service, and return events in one timeline.
-
Identity mismatches cause one asset to appear under serial number, hostname, device ID, purchase order line, and user-entered label without a reliable link.
-
Delayed synchronization makes a stale field look authoritative, especially at remote or low-connectivity locations.
-
Workflow handoffs break custody chains when employees, site administrators, couriers, repair vendors, and disposal partners use different processes.
-
Rules generate alerts but cannot reliably interpret conflicting evidence, policy exceptions, or the operational cost of each response.
-
Resolve the device identity across serial number, endpoint ID, hostname, purchase record, barcode, user assignment, and repair ticket.
-
Compare the last trusted custody event with later observations such as network presence, mobile-device check-in, building access, shipping scan, service-desk note, or stockroom receipt.
-
Evaluate timing and source reliability. A verified scan from a managed endpoint may outweigh an older spreadsheet entry, while a remote-site connectivity gap may explain missing telemetry.
-
Classify the case as stored, in transit, reassigned, under repair, awaiting disposal, potentially lost, or unresolved.
-
Select the next action: request confirmation, open a recovery task, correct a record, initiate a remote lock, suspend associated access, or escalate for investigation.
-
Apply the required approval based on asset sensitivity, data classification, employee status, geography, and financial policy.
-
Verify that the task is completed and that the CMDB, ITSM, endpoint, and inventory records now represent the same operational state.
-
Asset Identity Resolution Skill links device identifiers and flags uncertain matches for review.
-
Asset Reconciliation Skill compares system records and produces an evidence-backed current-state recommendation.
-
Custody Chain Validation Skill checks whether every transfer has a valid sender, receiver, location, and timestamp.
-
Return and Recovery Prioritization Skill ranks cases using data sensitivity, employee status, elapsed time, last known location, and replacement impact.
-
Disposition Verification Skill confirms that wipe, repair, redeployment, sale, donation, or destruction of evidence matches the approved lifecycle decision.
-
Establish the baseline and define the authoritative source for each field, the expected synchronization delay, and the evidence required for each disposition.
-
Build the minimum context graph for assets, person, site, custody event, endpoint observation, ticket, shipment, and policy.
-
Run the agent in recommendation mode and compare its decisions with experienced asset analysts.
-
Enable low-risk actions first, such as creating tasks and requesting confirmations, while retaining approvals for record changes and security actions.
-
Add outcome verification before expanding the scope. An action is incomplete until the target systems and operational reality agree.
-
Scale by publishing validated skills, onboarding additional sites and asset classes, and monitoring performance by workflow version.
Discovery scans alone cannot establish inventory accuracy or trustworthy IT asset visibility. A scan may prove that a device exists without establishing ownership, purpose, location, or custody. An assigned asset may also remain legitimately offline at a disconnected field site. Agentic AI IT asset management, therefore, requires both current state and temporal context so asset intelligence can distinguish delayed telemetry from genuine custody risk.
How Does Agentic AI Improve IT Asset Management and Asset Reconciliation?
An agentic operating model turns an IT asset exception into a governed sequence of observations, decisions, and verified actions. AI agents for IT asset management begin with a trigger such as an inactive owner, an overdue return, a conflicting location, a duplicate asset record, or a device that has stopped reporting. They then gather the context needed to classify the exception and perform evidence-backed IT asset reconciliation rather than immediately changing the system of record.
The operating sequence is Detect, Understand Context, Decide, Approve, Act, Verify, and Learn. Detect to identify meaningful deviations. Understand Context links the asset to its owner, location, purchase, service tickets, custody events, endpoint signals, and relevant policy. Decide selects the least risky next action and records the evidence. Approve applies to human oversight when the action affects security, finance, employment, or disposal. The act invokes the authorized enterprise workflow. Verify checks the outcome across the affected systems. Learn to use the result to improve future prioritization and exception handling.
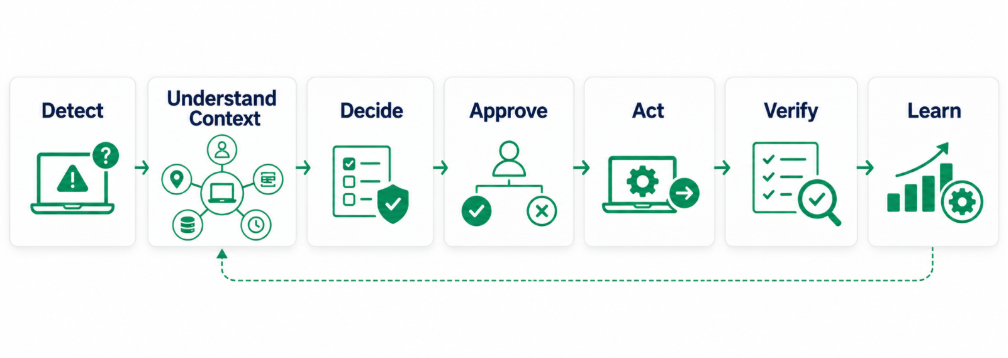
Figure 1: The governed Agentic AI loop for investigating and resolving an unaccounted IT asset.
This loop lets analysts spend less time assembling evidence and more time reviewing high-risk cases and improving policy. Automation remains bounded: agents can collect evidence and recommend a disposition broadly, while record changes, security actions, and lifecycle decisions remain constrained by policy and approval.
How Does the AI Workflow Find and Reconcile Lost IT Assets?
A useful workflow starts when a device misses its expected return date or when its assigned owner becomes inactive. The agent does not mark the asset as lost. It creates an investigation case and builds an evidence timeline using the asset's stable identifiers and known aliases. When a remote site reconnects, the agent can replay the event timeline, distinguish delayed updates from genuine exceptions, and prioritize assets whose custody or security posture remains uncertain.
What Is the Enterprise Architecture for AI-Powered IT Asset Management?
A scalable architecture for AI-powered IT asset management needs four cooperating planes. The integration plane acquires events and records from source systems without forcing an immediate system replacement. The context plane resolves asset identity and maintains current and historical relationships. The decision plane applies policies and reusable skills to each case. The execution plane invokes enterprise workflows through approved connectors and verifies outcomes. Governance spans every plane through identity, permissions, audit trails, policy evaluation, and human approval.
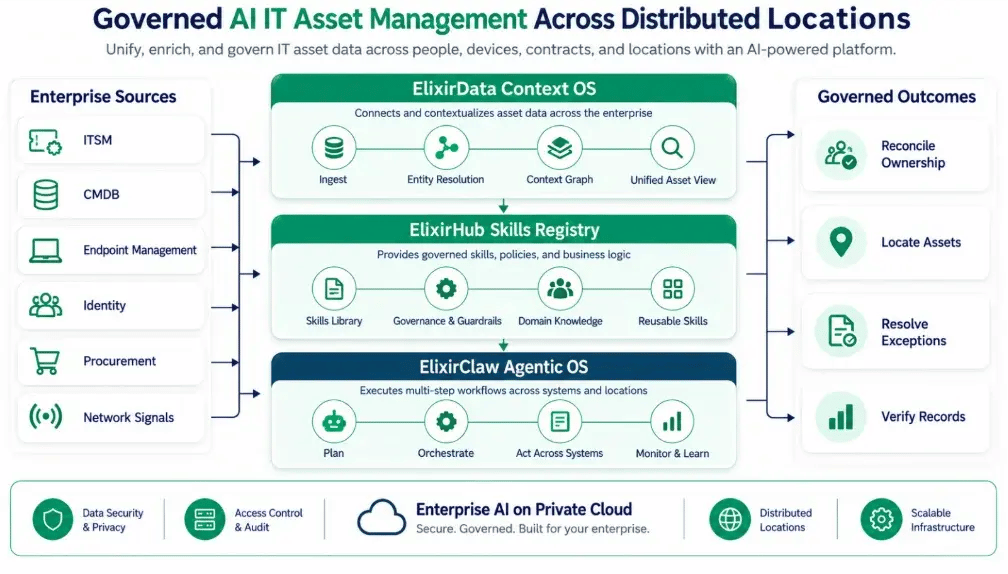
ElixirData, ElixirHub, and ElixirClaw provide context, governed skills, and controlled execution inside the enterprise boundary.
Source systems remain authoritative, while the context layer explains relationships and evidence. Skills hold reusable logic rather than embedding it in every agent. The execution layer cannot exceed agent or connector permissions, so improved reasoning does not require uncontrolled access to assets, identity, security, or financial systems.
Get the Executive Blueprint for governed enterprise AI
A practical guide for CIOs, CAIOs and risk leaders on moving AI agents from pilot to production without losing control of context or decisions.
How Does ElixirData Create Context for Asset Agents?
ElixirData acts as the Context OS for Agentic AI IT asset management and asset investigation. It ingests and synchronizes data from ITSM, CMDB, endpoint management, identity, procurement, ERP, network, logistics, repair, and disposal systems. Schema and field mapping normalize different representations of serial number, device identifier, employee, cost center, location, status, and timestamp. Entity resolution then determines which records refer to the same asset or custodian, creating the trusted asset intelligence required for reliable IT asset reconciliation.
An asset ontology gives those records operational meaning. It defines entities such as device, person, site, shipment, contract, ticket, software entitlement, repair order, and disposal certificate, along with relationships such as assigned to, observed at, shipped to, repaired by, covered by, and replaced by. ContextGraph connects those entities, while temporal context preserves when each relationship became valid and which event changed it.
Knowledge ingestion adds policies, operating procedures, warranty terms, return instructions, and site-specific rules. Graph intelligence follows relationships across systems; vector intelligence retrieves relevant unstructured notes and documents. Context retrieval provides the agent with the evidence relevant to the current case, while agent memory retains the investigation state without treating previous conclusions as permanent truth. This is how ElixirData creates a trusted enterprise context instead of a larger collection of disconnected records.
How Does ElixirHub Provide Reusable Operational Skills?
ElixirHub provides a governed registry for the operational skills used by asset agents. A skill packages a repeatable task, its inputs, policy assumptions, expected outputs, evaluation criteria, and version. Publishing and discovery allow teams to reuse approved logic across business units instead of recreating asset rules inside individual prompts or workflows.
Versioning is essential because policy and integration behavior change. The enterprise must be able to identify which skill version influenced a decision, compare results before promotion, and roll back a flawed update. Governance controls who can publish, approve, discover, or execute a skill. The same approved skill can then support asset-recovery agents, service-desk agents, audit assistants, and lifecycle-planning workflows.
How Does ElixirClaw Govern Execution?
ElixirClaw provides the Agentic OS that coordinates AI agents and multi-agent workflows. A triage agent can open the case, a context agent can assemble the evidence, a policy agent can evaluate decision boundaries, and an execution agent can invoke the approved action. Enterprise connectors and MCP interfaces expose only the tools required for the workflow, with scoped credentials and explicit permissions.
Agentic workflows can request a stockroom confirmation, update an ITSM task, correct a CMDB relationship, notify a manager, initiate a device lock, or route a case to security. Human approvals remain part of the workflow where the consequence requires judgment. Decision boundaries can depend on asset type, data sensitivity, evidence of confidence, geography, value threshold, and employee status.
Evaluations and AgentOps test whether agents classified cases correctly, used the right evidence, respected policy, and completed the expected verification. Agentic BI gives leaders a view of unresolved exposure, exception aging, recovery bottlenecks, and policy performance. Guardrails constrain tool use, data access, and workflow paths. Secure execution records the instruction, retrieved context, decision, approval, tool invocation, and verified result as one auditable trace.
Why Use Private Cloud AI for Secure Enterprise IT Asset Management?
IT asset investigations combine sensitive operational data that many enterprises cannot expose to a public execution boundary. The context may include employee identity, device telemetry, network location, software inventory, building information, purchase value, support history, security posture, and evidence related to termination or investigation. Even when each source system is approved, assembling those records for AI reasoning changes the risk profile.
Private cloud AI for IT asset management keeps models, context retrieval, agent memory, policy evaluation, and tool execution within the enterprise boundary. Data sovereignty controls can retain regional data in the required jurisdiction. Existing identity, privileged access, network segmentation, encryption, logging, and monitoring controls can govern the agent at runtime.
Private-cloud or on-premises deployment is relevant for plants, research environments, healthcare facilities, regulated supply chains, and remote operations. Local inference and context services can classify site exceptions during connectivity gaps and synchronize approved events later. Legacy CMDB, endpoint, ERP, and warehouse systems can remain inside approved networks.
Private AI controls where data and execution run. Access to policy, approvals, evaluation, and audit evidence still determines whether automation is accountable.
How Are Security Governance and Human Oversight Handled?
The safest design separates investigation authority from action authority. An agent may be allowed to read broadly enough to assemble context, but it should receive write access only to the systems and fields required for a defined workflow. High-impact actions should require explicit evidence and, where appropriate, human approval.
|
Decision class |
Example |
Expected control |
|
Low risk automation |
Create an investigation task or request site confirmation |
An agent may act within a predefined workflow and verify delivery |
|
Controlled record change |
Update the custodian after matching the handover evidence |
Confidence threshold, policy check, complete decision trace, and reversible write |
|
Security action |
Lock or wipe a device with uncertain custody |
Security approval, except for a separately approved emergency policy |
|
Financial or lifecycle action |
Retire, write off, or dispose of an asset |
Asset owner and finance approval with supporting evidence |
|
Prohibited autonomous action |
Change policy, expand permissions, or suppress audit evidence |
No autonomous path; administrative change control is required |
The decision trace should show which records were retrieved, their timestamps, the policy applied, the skill and model versions, confidence or uncertainty, approval of identity, tool calls, and verification result. This trace supports incident review and operational improvement. It also helps the enterprise detect agent drifts, connector failures, and policies that create too many false escalations.
Inventory controls also support security governance. NIST SP 800-53 control CM-8 addresses system component inventory, and CIS Control 1 focuses on the inventory and control of enterprise assets. Agentic asset operations can strengthen the evidence behind those controls, but they do not replace the enterprise's control ownership, risk assessment, or audit process.
What Are the Business Outcomes From Agentic AI IT Asset Management?
The value of Agentic AI IT asset management should be measured through operational outcomes and control quality, not the number of agent interactions. Enterprises should establish a baseline before automation and track results by asset class, location, and exception type. Useful measures include IT asset visibility, exception age, reconciliation accuracy, recovery time, manual effort, security exposure, and asset utilization. Directional outcomes include the following.
|
Outcome |
How the architecture contributes |
Evidence to monitor |
|
Fewer unaccounted assets |
Earlier detection and cross-system reconciliation shorten unresolved custody gaps |
Count and age of assets in unknown or conflicting states |
|
Faster remediation |
Agents assemble evidence, route owners, and execute approved workflows |
Time from exception detection to verified resolution |
|
Higher inventory accuracy |
Entity resolution and temporal context reduce duplicates and stale assignments |
Mismatch rate across CMDB, endpoint, procurement, and site records |
|
Lower manual effort |
Reusable skills perform repetitive searches and case preparation |
Analyst time spent per exception and rework caused by incomplete evidence |
|
Reduced security risk |
Custody uncertainty can trigger proportionate access and endpoint controls |
Unresolved high-sensitivity devices and overdue security actions |
|
Better utilization and cost control |
Recovered or idle devices can be redeployed before new purchases |
Available stock, redeployment cycle time, and avoidable purchase requests |
|
Stronger compliance evidence |
Decision traces link records, approvals, actions, and verification |
Completeness of custody and disposition evidence during control testing |
No credible business case should begin with an invented recovery percentage. The baseline will vary by asset type, location model, process maturity, and data quality. A pilot should therefore measure whether the architecture reduces exception age, improves the proportion of cases resolved with sufficient evidence, and lowers the amount of analyst effort required for each verified outcome.
What Is the Enterprise Adoption Approach for Governed Asset Operations?
Adoption should begin with one bounded exception class that already consumes measurable effort. Overdue employee returns, assets assigned to inactive users, or mismatches between CMDB and endpoint inventory are suitable starting points. The first phase should connect only the data needed to explain that exception and should operate in read-only mode while the enterprise validates entity resolution, evidence quality, and classification accuracy.
A successful pilot creates a governed asset ontology, reusable integration patterns, evaluation cases, decision boundaries, and a traceable operating process. These foundations support later expansion into maintenance, patch validation, warranty recovery, inventory optimization, and compliant disposition.
Conclusion: From Asset Exceptions to Governed AI Asset Management
Lost and unaccounted IT assets are a context and execution problem as much as an inventory problem. Effective Agentic AI IT asset management must determine which records refer to the same device, how custody changed over time, which evidence is current, which policy applies, and which action is permitted. A dashboard can expose the discrepancy; a governed agentic workflow can investigate it, reconcile the asset state, obtain approval, act across systems, and verify the result.
AgenticAssetOps provides an enterprise approach to AI asset management. ElixirData establishes decision-ready asset intelligence, ElixirHub makes operational logic reusable and governable, and ElixirClaw coordinates secure execution with human oversight. Deployed as private cloud AI or Enterprise AI on Private Cloud, the architecture keeps sensitive assets, employees, and operational data within the enterprise boundary while supporting autonomous asset operations where the organization is ready for them.
The practical objective is straightforward: reduce the time an asset remains unexplained, increase the evidence behind every custody and lifecycle decision, and give asset teams a controlled path from exception detection to verified resolution.
Take the next step
Download the Executive Blueprint, or talk to our team about governed agentic IT asset management.
Related Reading
- How Agentic AI Reconciles ITAM, CMDB and MDM Data
- Remote IT Asset Management with Agentic AI for Low-Connectivity Sites
- Beyond the Asset Register: Transforming Hardware Asset Management
Frequently asked questions
Why do IT assets go missing in distributed enterprises?
Rarely because one process failed. Several systems each hold a fragment of the truth, such as the service desk, endpoint management, HR and a courier record, and nobody reconciles them.
Why does traditional IT asset management fall short?
ITAM systems are valuable systems of record, but they depend on timely updates and process adherence. A record can describe a state without showing how it was reached or whether newer evidence contradicts it.
How does agentic AI improve asset reconciliation?
It turns an asset exception into a governed sequence of observations, decisions and verified actions, starting from a trigger such as an inactive owner, an overdue return or a conflicting location.
Does the agent mark a device as lost automatically?
No. It opens an investigation case and builds an evidence timeline from the asset's stable identifiers and known aliases before any decision is made.
What architecture does this need?
Four cooperating planes. They include an integration plane that acquires records from source systems without forcing a system replacement, a context plane that resolves asset identity and history, and a decision plane.